To secure your Linux virtual private server (VPS), protect administrative access and keep the operating system and software patched. Then limit unnecessary internet exposure and maintain backups you can restore.
VPS security means protecting your server, the software you run on it, and its data from unauthorized access, exploitation, malware, and data loss. On a self-managed VPS, you configure and maintain these protections yourself.
Follow these VPS hardening steps in order:
- Create a non-root account for administration.
- Set up SSH keys, then restrict password and root logins.
- Add Fail2Ban if you see repeated failed login attempts.
- Patch the operating system, packages, applications, and dependencies.
- Restrict inbound traffic with a firewall.
- Keep internal services from listening publicly.
- Protect app secrets and limit file and account permissions.
- Watch authentication, system, and app logs for suspicious activity.
- Scan for malware or unexpected files when relevant to your workload.
- Automate backups and test the restore process.
Is a VPS secure?
Yes, a VPS is secure at the infrastructure layer because virtualization isolates it from other VPS instances. Each VPS runs its own operating system and server environment, so other VPS users can’t access your accounts, files, or system configuration.
That isolation doesn’t automatically secure what runs inside your VPS, though. You still need to install security updates, secure SSH access, close unnecessary ports, and protect credentials stored by your apps.
Securing a VPS is a shared responsibility between you and your VPS provider. Your provider secures the infrastructure that runs and isolates the VPS, while you secure everything you install, configure, and expose on your server.
| VPS provider | VPS owner |
| Physical infrastructure | OS and package updates |
| Virtualization and VPS isolation | SSH and account security |
| Host networking | Firewall rules and exposed services |
| Provider-level security tools | App configuration |
| Management platform | Credentials, secrets, and permissions |
| Infrastructure-level protections | Monitoring and maintenance |
| Backup tooling | Backup configuration and restore testing |
Hostinger VPS hosting follows this model as a self-managed environment. Its VPS plans use Kernel-based Virtual Machine (KVM) virtualization, which gives each VPS its own kernel and allocated resources.
Hostinger handles the underlying infrastructure and provides management tools for firewall rules, malware scanning, backups, and recovery.
This VPS hardening baseline addresses three common risks: weak or stolen credentials, outdated software with known vulnerabilities, and services exposed to the internet unnecessarily.
Set up a VPS before applying the hardening steps if you haven’t finished the initial server configuration.
1. Create a non-root administrative user
Create a dedicated non-root administrative user by adding a new account to the sudo group on Debian and Ubuntu or the wheel group on Red Hat Enterprise Linux (RHEL)-family distributions.
You’ll use regular user permissions by default and run sudo only when a command needs administrator access.
This follows the principle of least privilege by giving each user only the permissions they need. It reduces the impact of accidental commands and limits how many accounts have unrestricted control over your VPS.
Review the current Linux user accounts before changing administrator access on an existing VPS.
Create a separate administrative account for each person who manages the server. Individual accounts let you revoke one person’s access without affecting other administrators and make sudo activity easier to trace to a specific user.
Keep your current root session open while you create and test the new account. Run the following commands as root, or add sudo before them if you’re already using another administrative account.
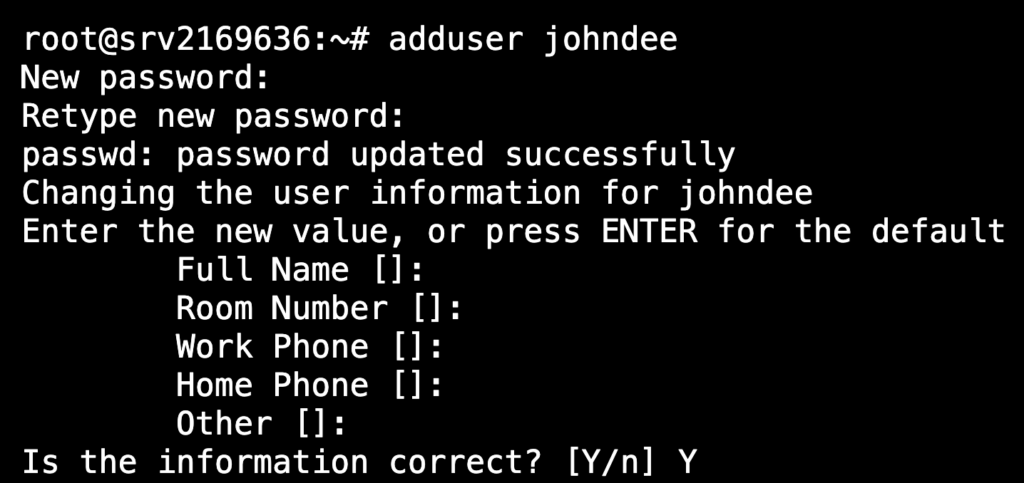
On Debian and Ubuntu, create the new user:
adduser your-username
The command creates the account and home directory, then prompts you to set a password and optionally enter user information before confirming the account details.
Confirm that your system has sudo before granting administrator access. Ubuntu includes it by default, while some Debian installations don’t:
command -v sudo
Install sudo if the command returns no path:
apt update
apt install sudo
Then add the newly created user to the sudo group:
usermod -aG sudo your-username
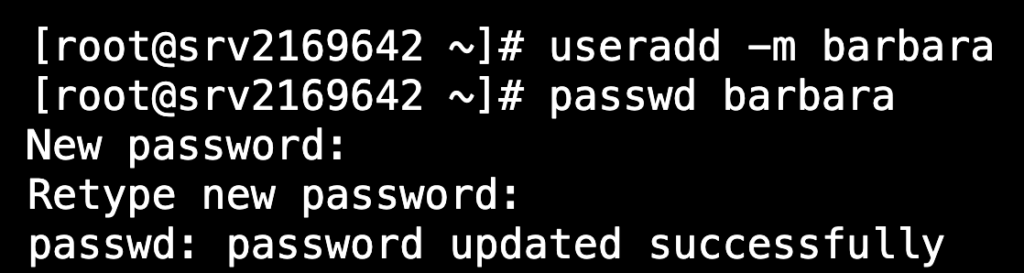
On RHEL-family distros, including RHEL, Rocky Linux, and AlmaLinux, create the user:
useradd -m your-username
Set its password:
passwd your-username
Then add the user to the wheel group, which grants sudo access on standard RHEL-family configurations:
usermod -aG wheel your-username
Verify the new account before restricting any existing administrator access. Switch to the new user and test sudo:
su - your-username
sudo whoami
Enter the new user’s password when prompted. The sudo whoami command should return root, confirming that the account has administrator access.
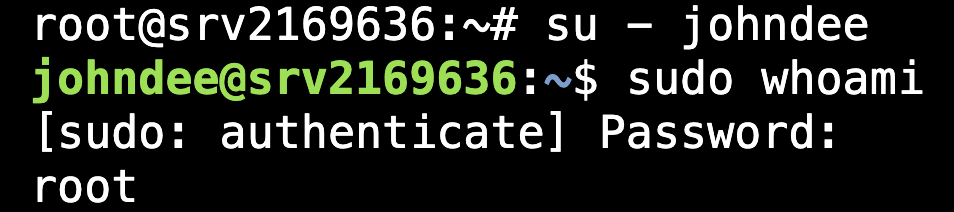
Fix the new account’s sudo access first if the command doesn’t return root.
2. Use SSH keys and restrict password and root logins
To use SSH keys, generate the key pair locally, add the public key to your non-root administrative account, and disable password authentication and direct root login only after you verify that key-based access works.
Keep your current SSH session open until you’ve tested the final configuration so you don’t lock yourself out.
Generate the key pair on your local computer and set up SSH keys for the non-root account you created earlier. Keep the private key on your computer and protect it with a passphrase.
From your local computer, copy the public key to your non-root administrative account, not only to root. A key added only to root won’t give you access once you disable root login later in this step.
Replace your-username with your non-root administrative username and your-vps-ip with your VPS IP address:
ssh-copy-id -i ~/.ssh/id_ed25519.pub your-username@your-vps-ip
Enter the non-root user’s password when prompted. Replace ~/.ssh/id_ed25519.pub if you saved the public key under a different file name.
Then open a second terminal window and confirm that key authentication works:
ssh -o PreferredAuthentications=publickey your-username@your-vps-ip
Continue only after the command logs you in with the non-root account. Keep this working key-based session and your original SSH session open while you change the authentication settings.
Create a separate SSH configuration file for the hardening settings using the nano text editor:
sudo nano /etc/ssh/sshd_config.d/00-hardening.conf
Set these values:
PubkeyAuthentication yes
PasswordAuthentication no
KbdInteractiveAuthentication no
PermitRootLogin no
PubkeyAuthentication yes keeps SSH key login enabled. PasswordAuthentication no disables password authentication, KbdInteractiveAuthentication no disables keyboard-interactive authentication, and PermitRootLogin no blocks direct SSH login as root.
Set KbdInteractiveAuthentication to yes instead if your multi-factor authentication (MFA) setup uses it for an additional verification step.
Save the file and exit nano by pressing Ctrl + X → Y → Enter.
Expert tip
OpenSSH reads files in /etc/ssh/sshd_config.d/ before the main sshd_config file and uses the first value it reads for most settings. Naming the file 00-hardening.conf makes it load before common later-named drop-in files, while sshd -T confirms the effective configuration before you reload SSH.

Minijus Savickas
VPS Product Manager
Check the configuration for syntax errors before applying the changes:
sudo sshd -t
No output means the configuration passed the syntax check. Fix any reported error before continuing.
Next, confirm which authentication settings OpenSSH will use:
sudo sshd -T | grep -E 'pubkeyauthentication|passwordauthentication|kbdinteractiveauthentication|permitrootlogin'
The output should show:
permitrootlogin no
pubkeyauthentication yes
passwordauthentication no
kbdinteractiveauthentication no
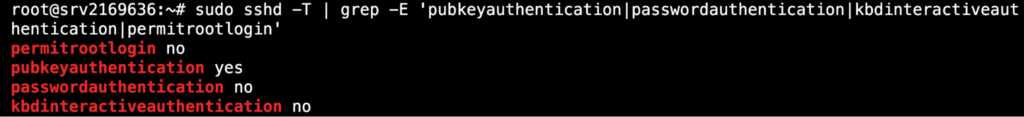
Don’t reload SSH if the output differs. Resolve the conflicting setting first, then run sudo sshd -t and sudo sshd -T again.
Reload SSH after both checks succeed. Run the following command on Debian and Ubuntu:
sudo systemctl reload ssh
Use sshd as the service name on RHEL-family distros:
sudo systemctl reload sshd
Open another local terminal and test the non-root account again:
ssh -o PreferredAuthentications=publickey your-username@your-vps-ip
Run sudo whoami after logging in. Close your original SSH session only after the key-based login succeeds and sudo whoami returns root.
Use Hostinger’s recovery options if an SSH configuration error locks you out. In the Hostinger dashboard, open VPS → Manage → Overview → Web console for browser-based server access.
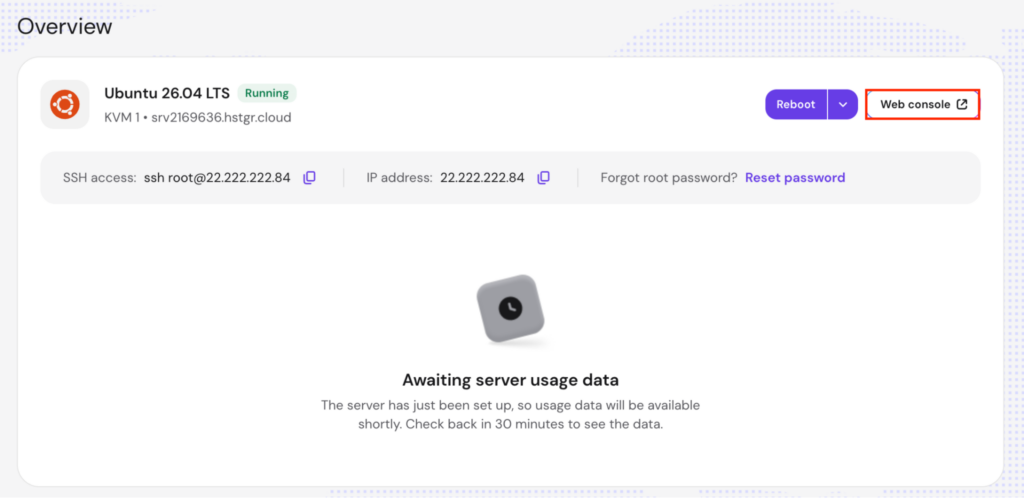
Hostinger Agent in the web console can also inspect the SSH configuration while troubleshooting the connection.
Alternatively, go to VPS → Manage → Settings → Main settings → Reset SSH to restore the default SSH configuration.
Use Reset firewall configuration in the same section to restore the default firewall rules if a Hostinger firewall rule blocks your SSH connection instead.
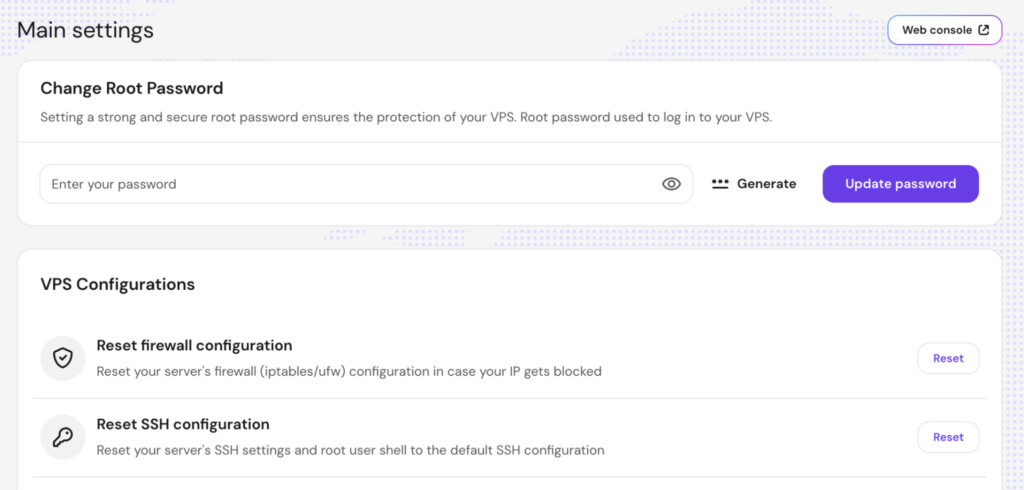
Use stronger access restrictions only when your setup requires them. Restrict SSH to trusted source IP addresses for administrators with fixed IPs, use a VPN to keep administrative access on a private network, or route access through a bastion host when you manage multiple servers.
Changing the SSH port also reduces automated scans and failed-login noise aimed at port 22. It doesn’t strengthen authentication or replace SSH keys or root-login restrictions.
Allow the new SSH port in every active firewall layer before switching. Otherwise, you can lock yourself out.
On Ubuntu systems that use systemd socket activation, changing the SSH port also requires reloading systemd and restarting ssh.socket for the new port to take effect.
3. Use Fail2Ban when there are repeated login attempts
Add Fail2Ban to SSH or another publicly reachable login service after you see repeated failed login attempts in its logs. Fail2Ban monitors those failures and temporarily blocks the source IP after the number of attempts reaches the configured retry limit.
For SSH, enable the sshd jail. A jail tells Fail2Ban which service to monitor and how many failed authentication attempts trigger an IP block.
Install Fail2Ban on Debian and Ubuntu with:
sudo apt update
sudo apt install fail2ban
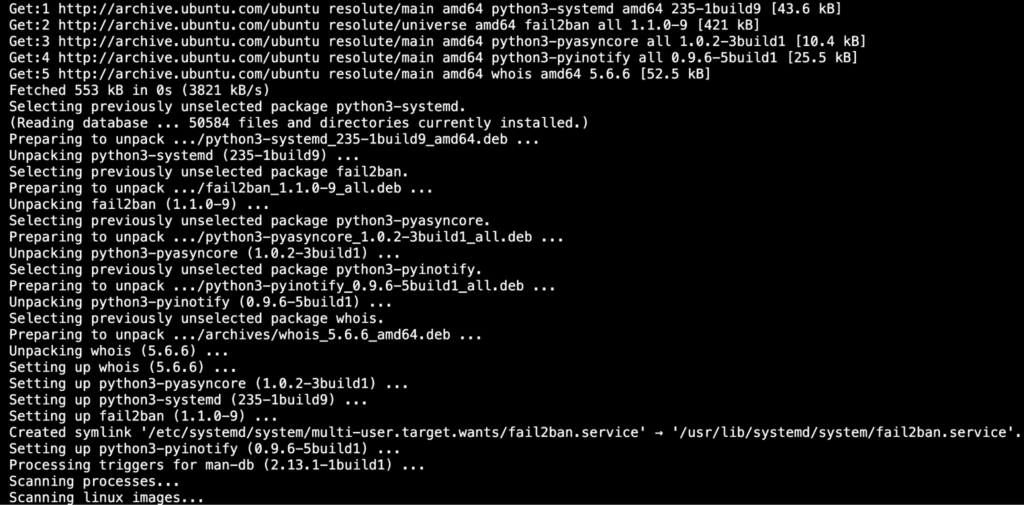
On RHEL-family distros such as Rocky Linux and AlmaLinux, enable the Extra Packages for Enterprise Linux (EPEL) repository first:
sudo dnf install epel-release
sudo dnf install fail2ban
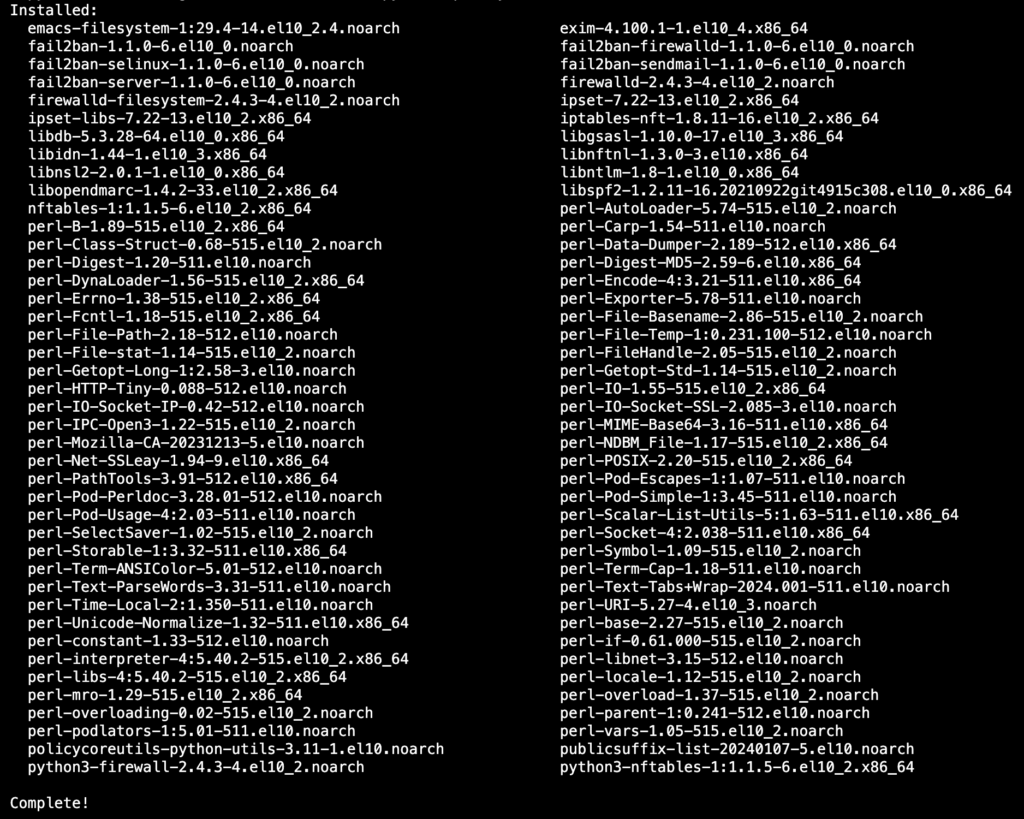
Create /etc/fail2ban/jail.d/sshd.local to enable the SSH jail without changing Fail2Ban’s default configuration files:
sudo nano /etc/fail2ban/jail.d/sshd.local
Add:
[sshd]
enabled = true
Save the file and exit nano. Fail2Ban will then watch SSH authentication failures and tell the server firewall to block an IP after too many failed attempts.
Keep your current SSH session open while testing so you still have access if Fail2Ban blocks your own IP.
Enable Fail2Ban at startup and restart it to apply the configuration:
sudo systemctl enable fail2ban
sudo systemctl restart fail2ban
Confirm that Fail2Ban is running:
sudo systemctl status fail2ban --no-pager
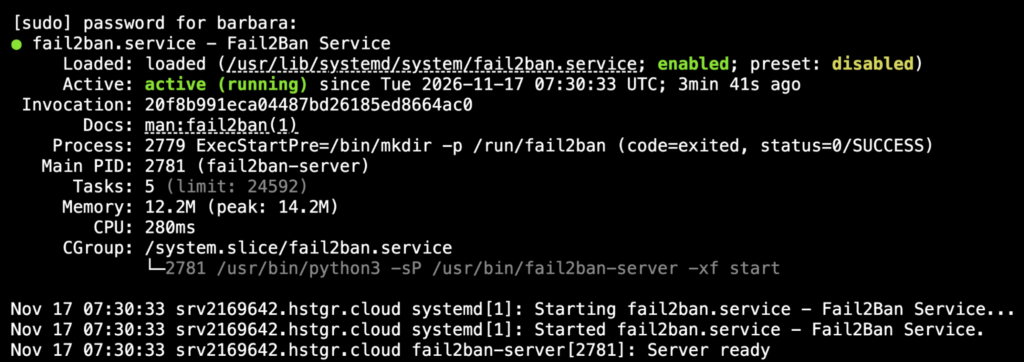
Continue when the output shows active (running), then check the SSH jail:
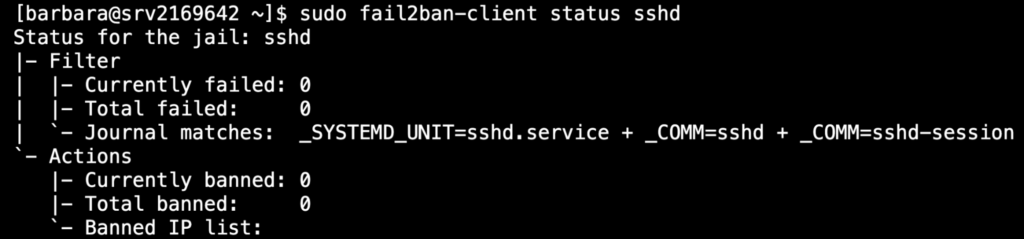
sudo fail2ban-client status sshd
The fail2ban-client status sshd command should show the sshd jail status and its failed-login and banned-IP counts.
Configure Fail2Ban further to allowlist trusted administrative IPs, adjust ban thresholds, or protect other login services that record authentication failures.
Fail2Ban complements SSH keys and firewall rules rather than replacing them. SSH keys strengthen authentication, firewall rules control which traffic reaches the VPS, and Fail2Ban reacts to repeated failed logins that still reach a monitored service.
However, Fail2Ban isn’t general DDoS protection. It blocks IPs only after matching events appear in server logs, so it won’t stop a large traffic flood before it reaches your VPS.
4. Keep the VPS and its software patched
Keep your VPS and its software patched by updating the operating system, system packages, apps, and dependencies as security fixes become available.
Refresh the available package list and install updates on Ubuntu and Debian with:
sudo apt update
sudo apt upgrade
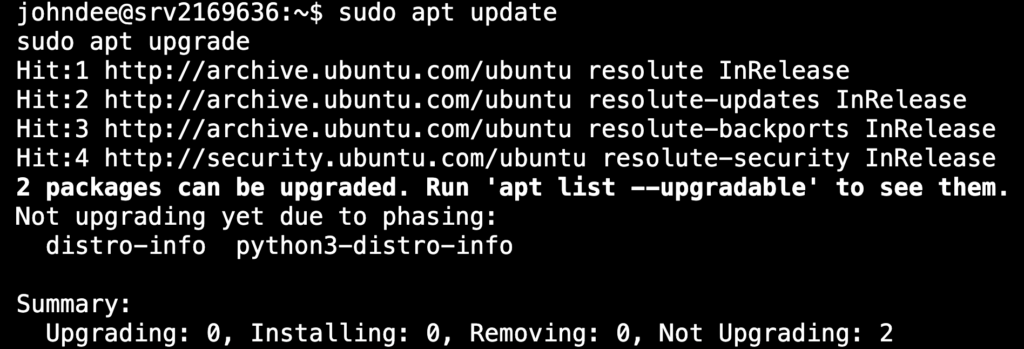
On RHEL-family distros, update installed packages with:
sudo dnf upgrade
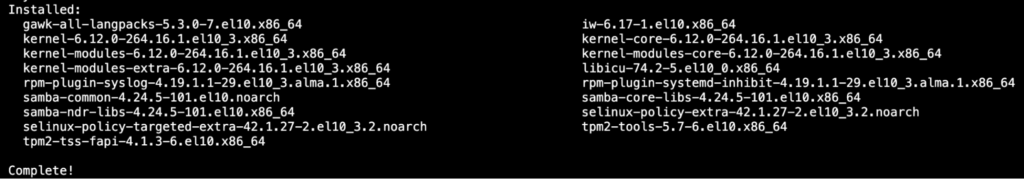
These commands update software installed through apt or dnf, including kernel packages when newer versions are available.
Review the proposed changes before confirming them, especially when they affect your web server, database, PHP, Node.js, or other software your site or app relies on.
Check whether the VPS needs a reboot after installing updates. On Debian and Ubuntu, check for the /run/reboot-required file:
test -f /run/reboot-required && cat /run/reboot-required || echo "No reboot required"
On RHEL-family distros, install dnf-plugins-core if needs-restarting isn’t available:
sudo dnf install dnf-plugins-core
Then check whether a reboot is required:
sudo dnf needs-restarting -r
Reboot the VPS when required:
sudo reboot
Plan the reboot for a low-traffic or scheduled maintenance period if temporarily taking the server offline would affect users.
Next, decide how you’ll keep the system patched over time. Automate security updates if you don’t need to review every update manually.
On Debian and Ubuntu, first check whether unattended-upgrades is installed:
dpkg -s unattended-upgrades
Install it if the command reports that the package isn’t installed:
sudo apt update
sudo apt install unattended-upgrades
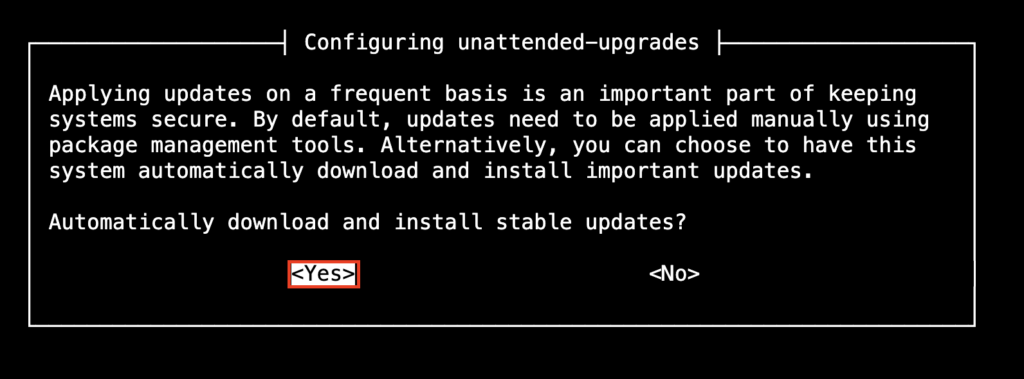
Then enable automatic updates:
sudo dpkg-reconfigure unattended-upgrades
Select Yes when prompted. This turns on automatic updates using the rules configured in unattended-upgrades.
On RHEL-family distros, install dnf-automatic:
sudo dnf install dnf-automatic
Open its configuration file:
sudo nano /etc/dnf/automatic.conf
Set upgrade_type = security under [commands] so it installs security updates rather than all available updates. Save automatic.conf, then enable its automatic update schedule:
sudo systemctl enable --now dnf-automatic-install.timer
Keep security updates manual if you prefer to review changes before installing them. This gives you more control over updates that could affect your site or app.
Also check that your Linux release still receives security updates. Find the installed distro and version with:
cat /etc/os-release
Upgrade to a supported OS release before your current version stops receiving security updates. Depending on your distro and hosting setup, you can either perform an in-place release upgrade or reinstall the VPS with a newer supported OS.
On Ubuntu Server, for example, moving from one Long Term Support (LTS) release to the next is a separate OS upgrade rather than a normal apt upgrade:
sudo do-release-upgrade
Treat a major OS upgrade more carefully than routine package updates because it can remove packages, change configuration files, or make existing apps incompatible.
Review the new release notes and take a snapshot of your VPS before starting the upgrade so you have a recovery option if something breaks.
System updates only cover software installed through apt or dnf. A patched operating system can still run vulnerable apps, plugins, libraries, or containers that you need to update separately.
For example:
- Update content management system (CMS) cores, themes, and plugins through the CMS itself or its supported command-line tool.
- Check Node.js dependencies with npm outdated, Python packages with
python -m pip list --outdated, and PHP dependencies managed by Composer with composer outdated. Apply dependency updates to a staging copy first when possible, then check that the app starts, its main functions work, and the logs show no new errors. - Update manually installed apps and control panels using their vendor-supported update process.
- Update container images and recreate the affected containers because updating the VPS itself doesn’t update software inside existing container images.
5. Configure a firewall
Configure your VPS firewall to block unsolicited inbound traffic by default, then allow only the ports required by the services you expose.
Start by checking which services are listening for network connections:
sudo ss -tulpn
Check the Local Address and process for each entry. An address of 0.0.0.0 means the service listens on all IPv4 addresses assigned to the VPS, [::] means it listens on all IPv6 addresses, and 127.0.0.1 or ::1 limits access to the VPS itself.
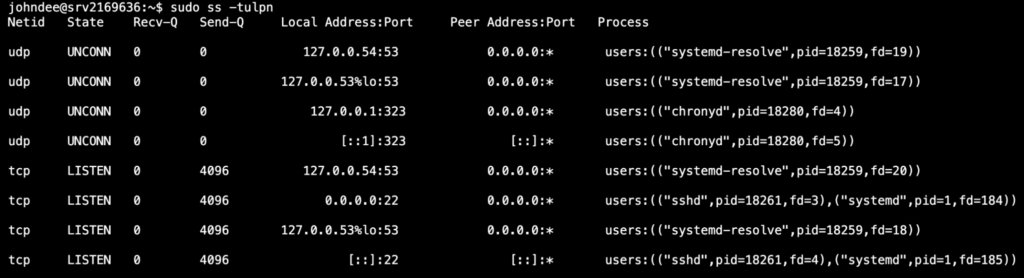
Decide which listening ports need connections from outside the VPS. For example, a database used only by an app on the same VPS doesn’t need a public firewall rule.
On Ubuntu and Debian, configure Uncomplicated Firewall (UFW) by denying incoming connections by default while allowing outgoing traffic:
sudo ufw default deny incoming
sudo ufw default allow outgoing
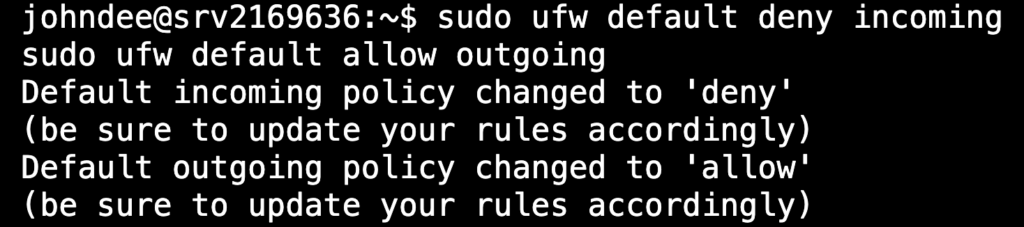
Allow SSH before enabling UFW so you don’t lock yourself out. Use the OpenSSH profile when SSH uses its standard port:
sudo ufw allow OpenSSH
Allow the actual SSH port instead if you’ve changed it:
sudo ufw allow your-ssh-port/tcp
Add rules only for other services that need public access. A web server, for example, normally needs TCP ports 80 for HTTP and 443 for HTTPS:
sudo ufw allow 80/tcp
sudo ufw allow 443/tcp
Skip these rules when the VPS doesn’t serve web traffic. Allow only the port and protocol that external users or systems need for every other service.
Enable UFW and review the active rules:
sudo ufw enable
sudo ufw status verbose
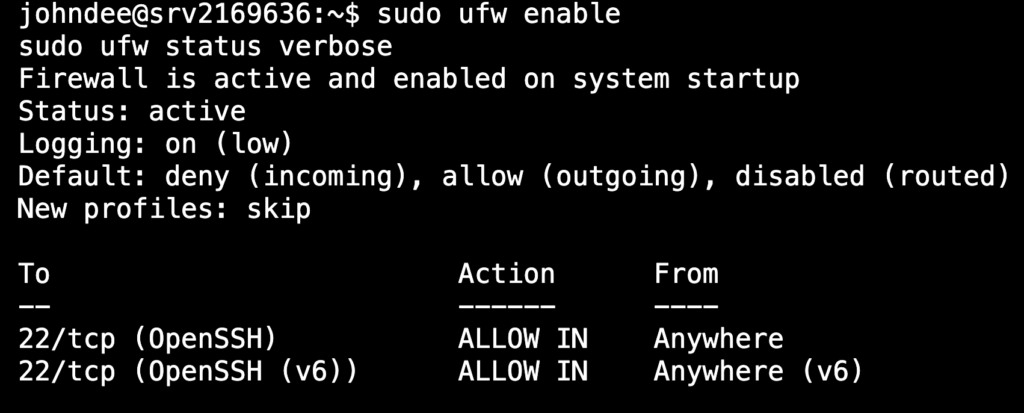
Keep your current SSH session open and test a new SSH connection from another terminal before closing it. Test other allowed services as well, such as loading your website after opening ports 80 and 443.
Remove firewall rules after you stop exposing the service they belong to. List numbered UFW rules first with:
sudo ufw status numbered
Then remove the obsolete rule by replacing rule-number with its number:
sudo ufw delete rule-number
Apply the same firewall protection to IPv6 instead of disabling IPv6 by default. Check whether UFW manages IPv6 with:
grep '^IPV6=' /etc/default/ufw
Keep IPV6=yes when your VPS uses IPv6. UFW then applies the rules you create to both IPv4 and IPv6 traffic.
For more advanced rule control on Ubuntu or Debian, use iptables when you need features such as custom rule ordering or port forwarding.
On RHEL-family distros, use firewalld for typical host firewall rules or nftables for more advanced configurations.
Avoid managing the same host firewall through multiple tools at once because overlapping UFW, firewalld, nftables, or manual iptables rules make the active policy harder to understand and troubleshoot.
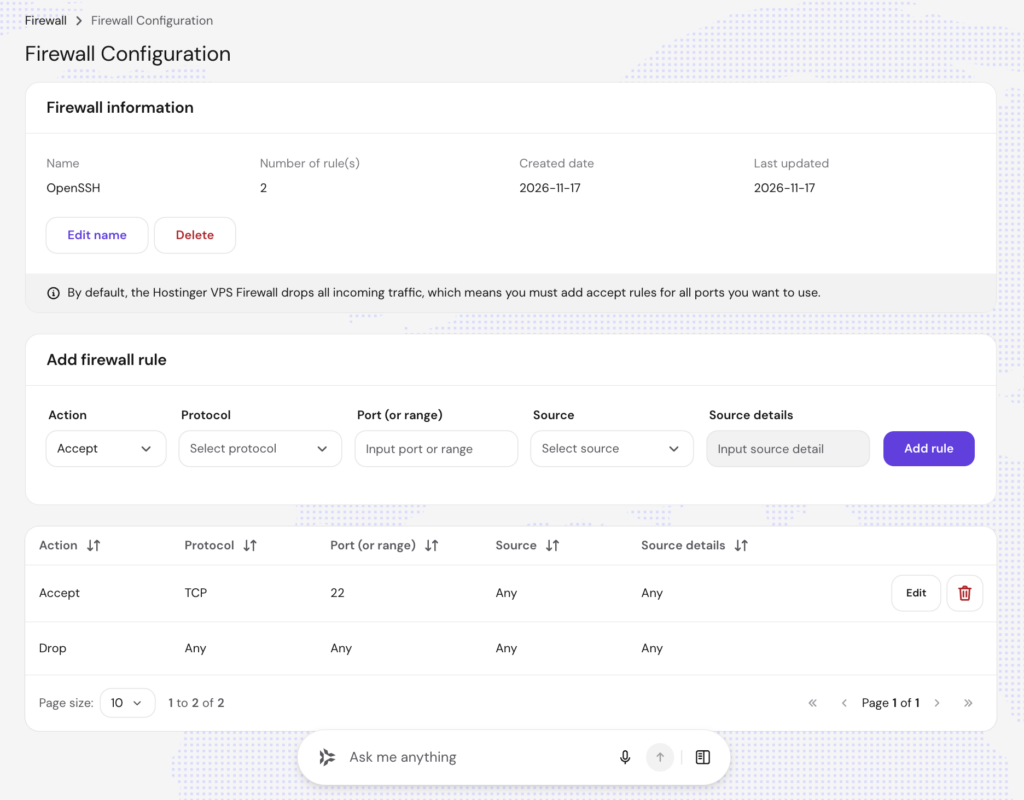
The Hostinger VPS firewall filters incoming traffic before it reaches your VPS. It isn’t active until you create a firewall configuration and activate it for your server.
Open VPS → Manage → Security → Firewall, create a firewall group, and add an accept rule for SSH before activating it.
Add accept rules for the other public services you identified earlier. For example, a web VPS using SSH on port 22 typically allows TCP ports 22, 80, and 443.
Watch this video if you prefer a visual walkthrough of how to set up a firewall in the Hostinger dashboard:

The firewall drops incoming traffic that doesn’t match an accept rule, so add the SSH rule before activation to avoid blocking remote access. After you add, change, or remove a rule later, sync the firewall so the updated configuration applies to your VPS.
Check both firewall layers when you combine the Hostinger firewall with UFW. SSH will still fail if UFW allows port 22 but the Hostinger firewall blocks it, while HTTPS will fail if the Hostinger firewall allows port 443 but UFW blocks it.
Use Hostinger Agent to inspect the firewall configuration when a required connection stops working after a rule change. Compare the rules for the affected port before adding new exceptions.
Expert tip
Using Docker? Published container ports can remain reachable from the internet even when UFW blocks them because Docker manages its own firewall rules. Keep an internal service private by binding its published port to localhost, for example 127.0.0.1:8080:80 instead of 8080:80 in your Docker Compose file, and use the Hostinger VPS firewall to control which public ports remain reachable.
Minijus Savickas
VPS Product Manager
6. Restrict publicly accessible services
To restrict publicly accessible services, make databases, caches, admin panels, development tools, and other internal services listen only on localhost or a private network unless they genuinely need public access.
Check which TCP services are listening for connections:
sudo ss -tlnp
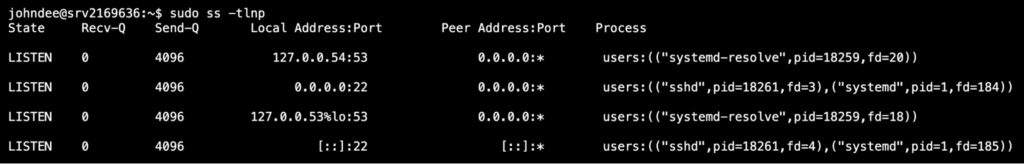
Use the Local Address and process information to find databases, caches, admin tools, and other internal services that are listening publicly. Focus on services that don’t need connections directly from the internet.
To keep an internal service off the public internet, change the address it listens on to 127.0.0.1, ::1, or a private IP. For example, make a database listen on 127.0.0.1 when only an app on the same VPS connects to it.
Secure the publicly accessible service instead of restricting it to a private IP when it must remain reachable from the internet.
Use a private IP instead when another server on the same private network needs access. Configure the listening address with bind-address for MySQL, listen_addresses for PostgreSQL, bind for Redis, or net.bindIp for MongoDB.
Restart the affected service after changing its configuration, then run sudo ss -tlnp again to confirm that it listens only on the intended address.
Disable services you no longer use so they stop running and don’t start again after a reboot. Replace service-name with the actual service name:
sudo systemctl disable --now service-name

Remove unused software after confirming that your site or app doesn’t depend on it. On Debian and Ubuntu, use:
sudo apt remove package-name
On RHEL-family distros, use:
sudo dnf remove package-name
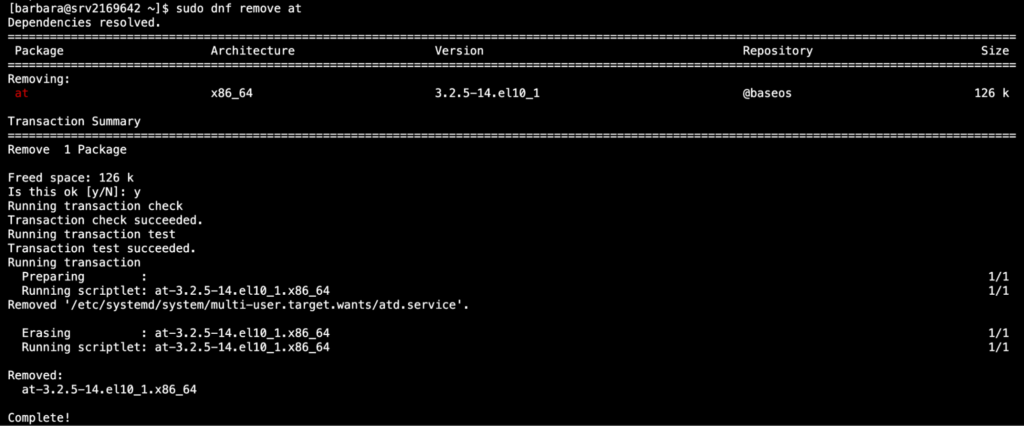
Remove old test dashboards, development servers, database engines, and other tools after you stop using them.
Use an SSH tunnel when you need occasional remote access to a service that should remain on localhost. For a service listening on 127.0.0.1:8080, run this command on your computer:
ssh -L 8080:127.0.0.1:8080 your-username@your-vps-ip
You can then access the service through localhost:8080 on your computer while the SSH connection remains open, without exposing the service itself to the internet.
For other remote-access needs, restrict the service to a trusted source IP when you connect from a fixed public IP, use a private network or VPN for access from trusted devices, or place a browser-based admin tool behind an authenticated HTTPS reverse proxy.
Choose the option that keeps the service itself off the public internet.
Encrypt connections for services that must remain publicly accessible. Use HTTPS for websites and web interfaces, SFTP for secure file transfers, and TLS for remote database connections that cross the public internet.
Run sudo ss -tlnp again after making the changes. Confirm that internal services no longer listen publicly and that the services or remote-access methods you intentionally kept still work.
7. Protect app credentials and file permissions
Protect app credentials and file permissions by keeping secrets out of source code, locking down files that contain them, and running apps with only the access they need.
API keys, database passwords, access tokens, private keys, and similar credentials shouldn’t appear directly in your app’s source code. Store them in Linux environment variables, a protected .env or configuration file, or a secret-storage tool your app supports.
A .env file stores values such as database passwords and API keys separately from your source code. Keep it and other files containing secrets outside directories that visitors can access through your web server.
Keep secret files out of source repositories as well, since committing them can expose credentials to anyone who can access the repository or its history. For Git projects, add .env to .gitignore:
.env
Check whether Git already tracks the file:
git ls-files .env
Remove it from Git tracking without deleting your local copy if the command returns .env:
git rm --cached .env
Removing the file from Git doesn’t make an exposed credential safe again, because it stays in the repository’s history.
Replace any password, API key, access token, or private key that you’ve already committed to Git, uploaded, or shared, then update the app to use the replacement and disable the old credential.
Use different credentials for separate apps and services. For example, give an app its own database user with access only to the database it needs instead of using a database administrator account.
Next, restrict access to files that contain secrets. Replace /path/to/app/.env with the actual path to your app’s .env file, then check the file’s permissions, owner, and group:
ls -l /path/to/app/.env

Use 600 when only the file owner needs to read and edit it:
chmod 600 /path/to/app/.env
Use 640 when the owner needs read and write access and the app runs under a group that also needs to read the file:
chmod 640 /path/to/app/.env
Set the correct owner and group when necessary:
sudo chown your-owner:app-group /path/to/app/.env
Replace your-owner with the account that manages the file and app-group with the group allowed to read it.
Run ls -l /path/to/app/.env again after changing its ownership or permissions. Confirm that only the intended owner and group can access the file.
Avoid using chmod 777 to fix permission errors. It gives every local user read, write, and execute access, which is far more access than secret files or most app files need.
Limit the permissions of accounts that run your apps as well. Run apps, background workers, and containers as non-root users unless they need root access for a specific task.
Check which user runs each process with:
ps -eo user,pid,comm
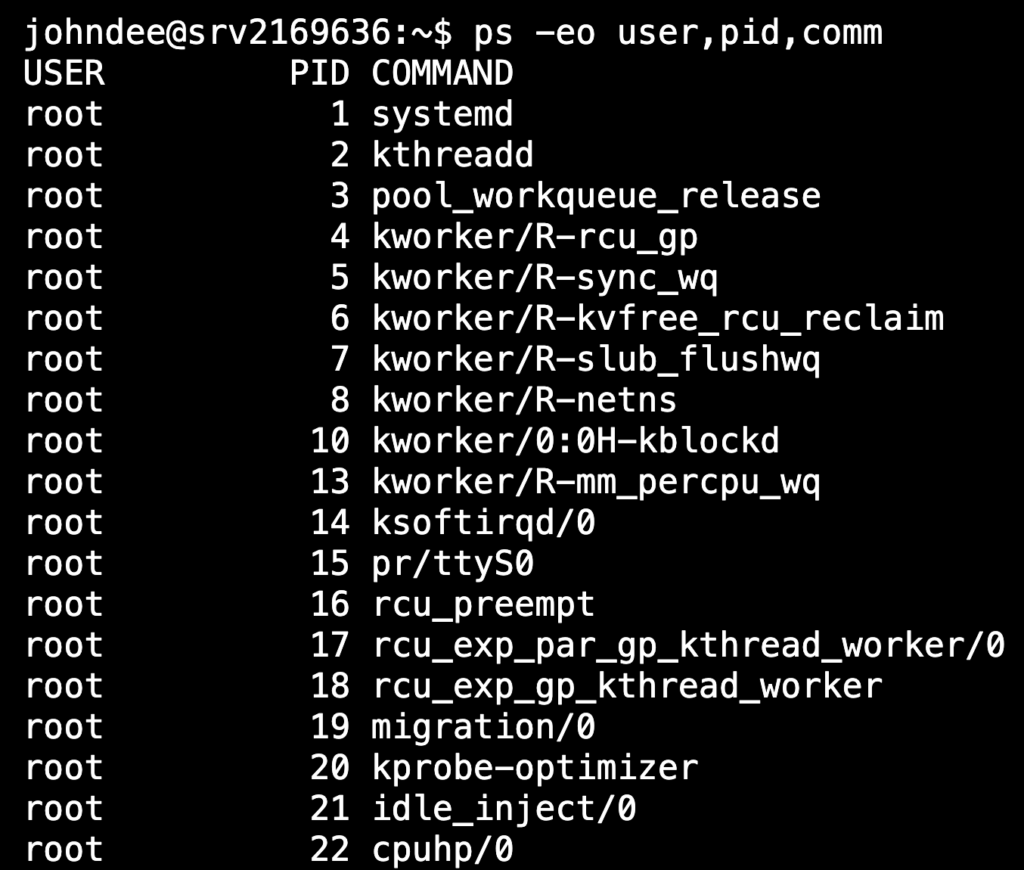
Find your app or worker in the output and check the USER column. Change its configuration if it runs as root without needing full system access.
For a systemd service, assign an existing non-root account with:
sudo systemctl edit service-name
Add:
[Service]
User=app-user
Group=app-group
Make sure the account can access only the files and directories the app needs, then restart the service:
sudo systemctl restart service-name
Configure containers to run as a non-root user instead of using root by default.
Use separate service accounts for unrelated apps that shouldn’t share access to the same files. Keep these app accounts out of sudo and wheel groups unless they specifically need administrative commands.
8. Monitor server and app logs
Monitor authentication, system, and app logs for activity that doesn’t match the users, services, and workload you expect on your VPS.
Start by reviewing recent system and service messages using this journalctl command:
sudo journalctl --since today
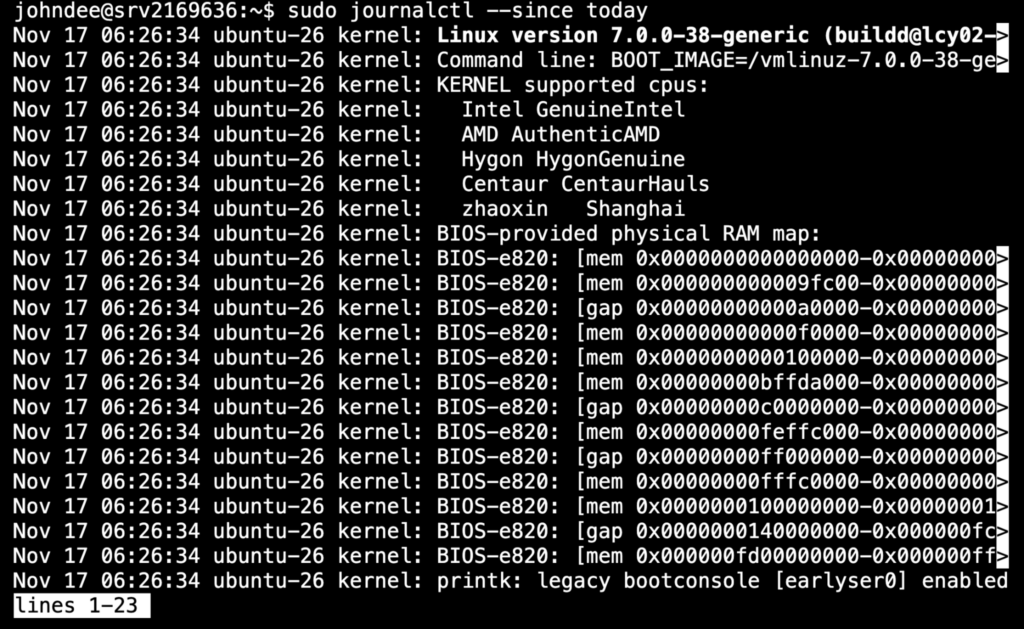
Check SSH logs separately to review login activity. On Debian and Ubuntu, use the ssh service unit:
sudo journalctl -u ssh --since today
On RHEL-family distros, use the sshd service unit:
sudo journalctl -u sshd --since today
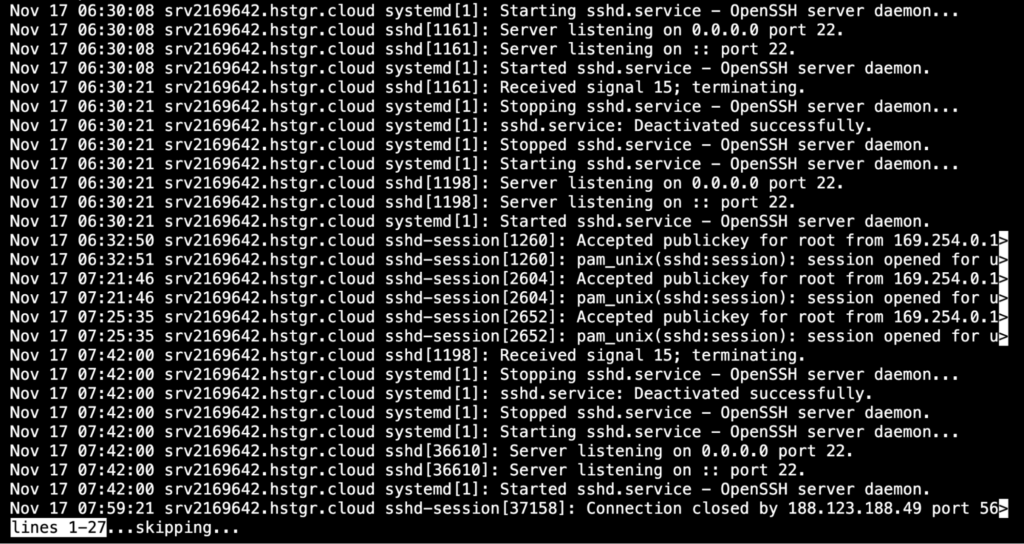
Check sudo activity to review administrative commands:
sudo journalctl _COMM=sudo --since today
Next, review logs for the services that run your site or app. Replace service-name with the service you want to inspect:
sudo journalctl -u service-name --since today
Web servers also keep their own access and error logs. NGINX commonly uses /var/log/nginx/access.log and /var/log/nginx/error.log, while Apache commonly uses /var/log/apache2/ on Debian and Ubuntu or /var/log/httpd/ on RHEL-family distros.
Check your app and database logs too. Their locations depend on how you installed and configured them, so use the log path each service uses.
To check whether your VPS may have been compromised, review its logs and current activity for:
- Repeated failed logins or successful logins you don’t recognize.
- Unexpected sudo activity.
- Administrator activity followed by new user accounts or SSH keys you didn’t add.
- New services or listening ports you don’t recognize.
- App, web server, or database errors that suddenly appear or repeat.
- Suspicious outbound connections.
- Unexpected CPU, memory, disk, or network usage that appears alongside other suspicious activity.
Compare events by time instead of treating every warning as a separate problem. An unfamiliar login followed by unexpected sudo activity and new app errors is more concerning than one failed login attempt.
Set alerts for problems that need quick attention, such as a service stopping, disk space running low, or unusual resource usage, when your monitoring tool supports them. Check logs from the same time as the alert to find the cause.
Keep file-based logs from growing indefinitely and filling the VPS disk. Check which logs logrotate already manages without changing anything:
sudo logrotate --debug /etc/logrotate.conf
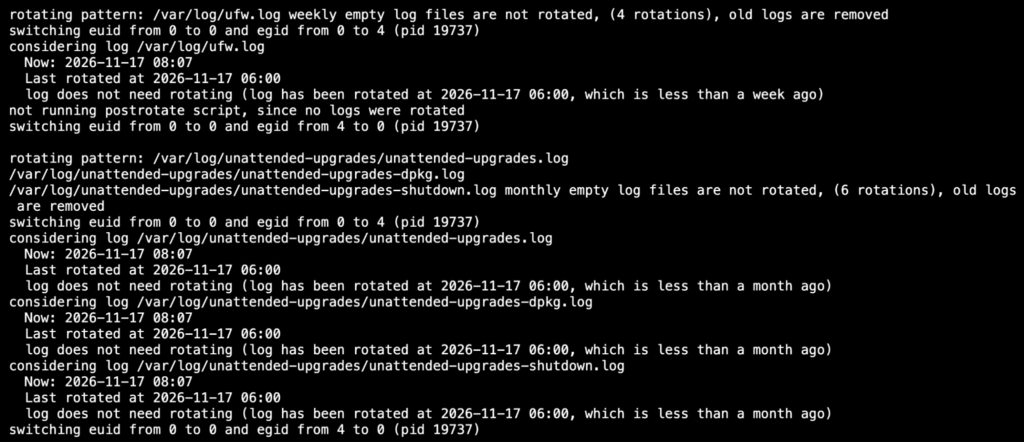
Confirm that important web server and app log paths appear in the output. Add a rotation rule under /etc/logrotate.d/ for a custom app log that logrotate doesn’t already manage, unless the app handles rotation itself.
On Hostinger VPS, Hostinger Agent can inspect logs from the web console while you troubleshoot. For example, ask it to review recent SSH failures or errors from a specific service instead of searching through multiple logs manually.
Use centralized logging when you manage several VPSs or need an independent copy of important logs. A Loki, Grafana, Tempo, and Mimir (LGTM) stack is one option for collecting and searching logs from multiple systems.
Keep the centralized copy on another server or managed logging service when you want it to remain available after a VPS compromise. This also preserves the logs if someone deletes or overwrites the originals.
9. Scan for malware or unexpected files when appropriate
Scan for malware and unexpected files when your VPS handles public-facing apps, accepts file uploads, or otherwise receives untrusted content.
Malware scanning checks files directly for known threats that regular log monitoring doesn’t inspect. Reviewing unexpected file changes also helps you investigate a suspected compromise.
Investigate files you didn’t create, scripts that appear in unexpected directories, or files that changed without an update or deployment. To list files modified within the last 24 hours in an app directory, run:
find /path/to/app -type f -mtime -1 -print
Replace /path/to/app with the directory you want to inspect.
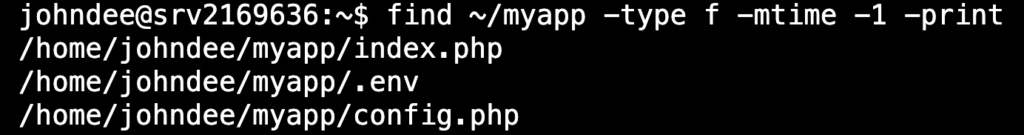
A recently changed file isn’t automatically malicious, so compare unfamiliar changes with updates, deployments, or other activity you expected during the same period.
On Hostinger VPS, open VPS → Manage → Security → Malware Scanner to install and run its Monarx-powered malware scanner. Review any files it flags as compromised or malicious before deciding what to remove or replace.
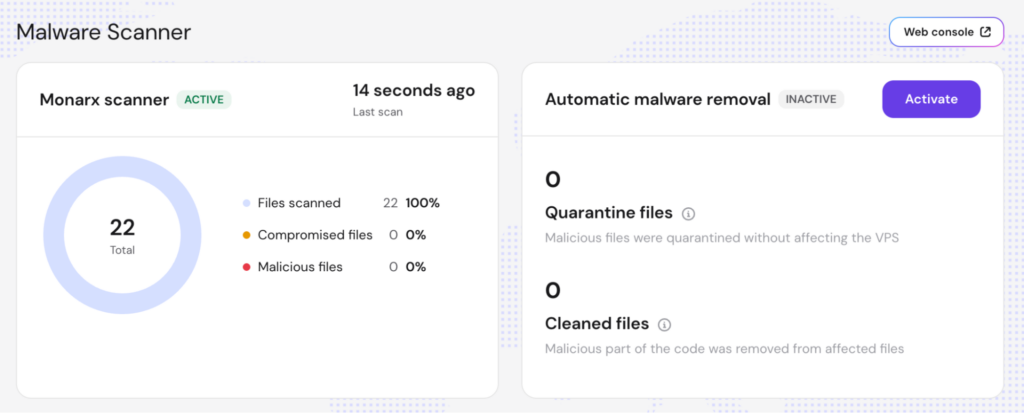
The malware scanner checks files stored on the VPS but doesn’t scan database contents. A clean scan doesn’t rule out every type of compromise.
You can review detections and clean up affected files manually without a paid Monarx license. Automatic malware cleanup is a separate paid feature, though.
Alternatively, use an open-source antivirus scanner such as ClamAV. Install it on Debian and Ubuntu with:
sudo apt update
sudo apt install clamav
On Rocky Linux and AlmaLinux, enable the EPEL repository and install ClamAV:
sudo dnf install epel-release
sudo dnf install clamav
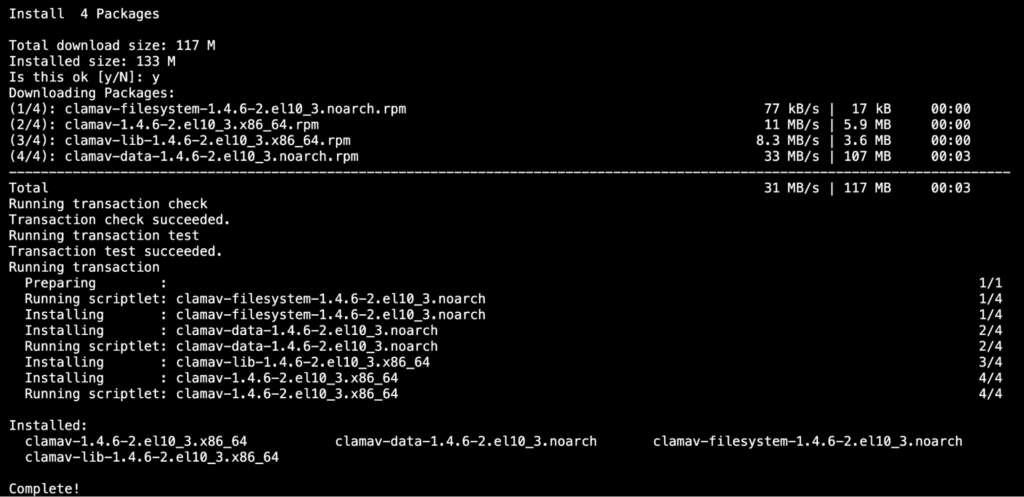
On RHEL, enable the matching EPEL repository first, then install the same packages:
sudo dnf install clamav
Scan the file or directory you want to check after installing ClamAV:
clamscan --recursive /path/to/suspicious-directory
Replace /path/to/suspicious-directory with the actual location.
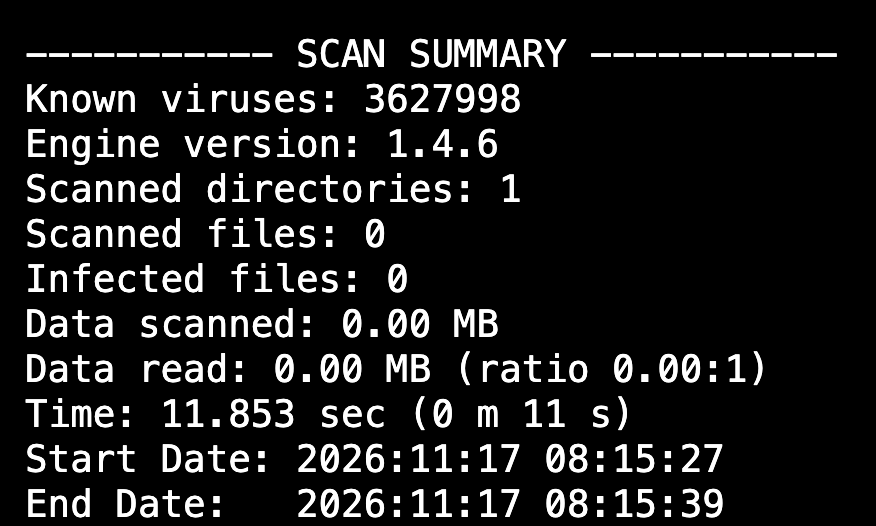
Review detected files before deleting them because scanners sometimes flag legitimate files.
Regardless of the scanner you use, malware scanning complements patching, secure authentication, firewall rules, service restrictions, and log monitoring rather than replacing them.
10. Maintain automated backups and test restores
Maintain automated VPS backups by keeping recurring backups enabled. Then test restores regularly to confirm that you can restore a working server after file deletion, data corruption, or other server problems.
Recurring backups run automatically on a schedule and give you copies from different dates. Choose the backup frequency based on how much recent data you can afford to lose.
A frequently changing store, forum, or app usually needs more frequent backups than a mostly static website because more orders, uploads, or database changes occur between backups.
A snapshot captures the VPS at one specific moment so you can return to that state if a planned change causes problems. Use snapshots before major updates, migrations, operating system changes, or risky configuration changes.
Unlike recurring backups, snapshots don’t provide an ongoing history of recovery points. They’re better suited to short-term protection around a specific change.
On Hostinger VPS, manage VPS backups and snapshots from VPS → Manage → Backups & Monitoring → Snapshots & Backups.
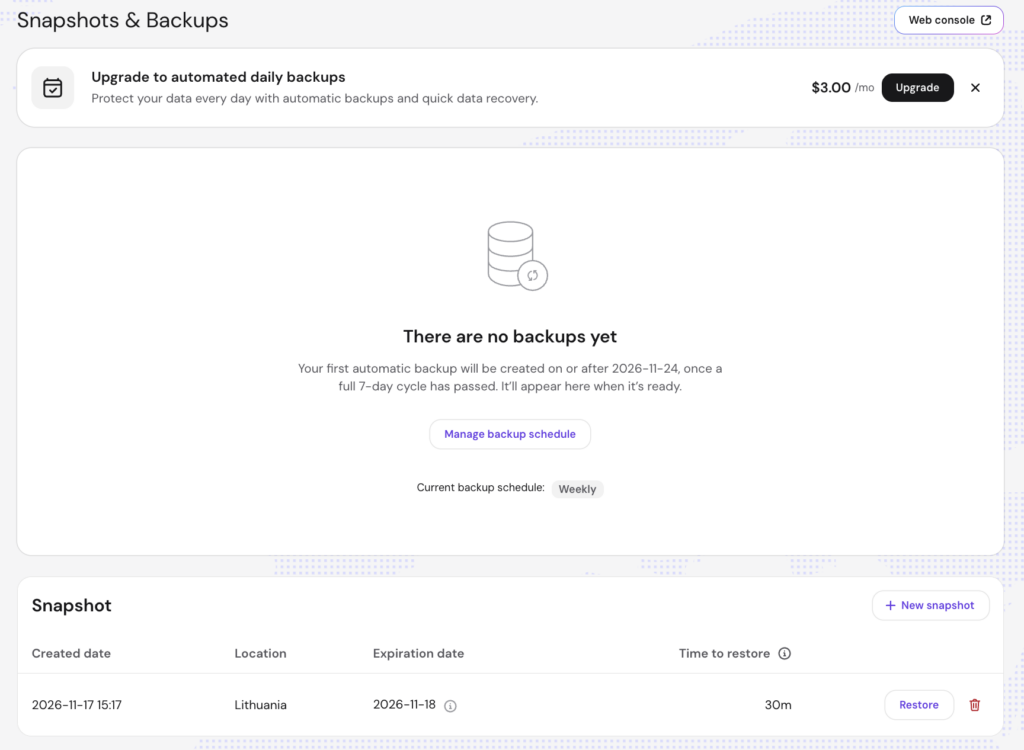
Hostinger enables weekly automated backups by default. You can upgrade to daily backups if you need more frequent recovery.
Hostinger stores automated backups separately from your VPS. It stores only one snapshot at a time on the VPS server and deletes it automatically after one day.
Keep another copy of critical data on a different server or storage service when you need a backup independent of your VPS provider’s backup system.
For example, use rsync to copy critical files to another Linux server, including database exports, uploaded files, or other app data that would be difficult to recreate.
Use app-level backups when you need to restore one component without rolling back the entire VPS. A separate database backup, for example, lets you recover database data without replacing the rest of the server.
Test restores in a separate environment whenever possible so you don’t disrupt the live VPS. Restore the backup there, then check whether the recovered workload works.
Verify the following after restoring:
- Required files and directories are present.
- Databases restore correctly and contain the expected data.
- Apps and supporting services start successfully.
- Required configuration files are available.
- File ownership and permissions are correct.
- You can restore required passwords, API keys, certificates, and other secrets securely.
- The restored site, app, database connections, background jobs, and other important functions work as expected.
Fix anything the restore test shows is missing. For example, add database backups to your backup process and test again if the files restore correctly but the database doesn’t.
Write down the restore order for apps that depend on several components. For example, you may need to restore the files first, then the database, configuration, and secrets, and finally start the required services.
How do you maintain VPS security over time?
To maintain your VPS security over time, turn the initial hardening into a routine you repeat on a schedule and after security-related changes.
Start by writing down what your normal VPS setup should look like. Note who should have administrator access, which ports and services should be public, which apps require regular updates, which logs you rely on, and what your backups cover.
Use that record during future reviews to spot anything that changed unexpectedly or no longer matches how you use the server.
Start with a monthly review. Move to weekly reviews for a VPS with frequent deployments, user changes, configuration changes, or new public services.
Each scheduled review covers five checks: pending updates, user accounts and SSH keys, listening ports and firewall rules, recent log activity, and the latest successful backup.
You don’t need to repeat every hardening check after every change. Focus only on the security checks affected by what changed:
- Review administrator access after adding or removing an administrator or changing authentication.
- Review firewall rules and listening services after opening a port or deploying a service that accepts network connections.
- Review credentials, permissions, logs, and backups after deploying or migrating an app.
- Review affected services and their configuration after a major OS or app upgrade.
Run the relevant checks immediately after these changes instead of waiting for the next scheduled review.
Keep a short record of important security-related changes. Note what changed, who changed it, when it happened, and which checks you ran afterward so you can trace unexpected settings later.
VPS hardening secures the server itself, but each app you install brings its own security requirements. Keep a separate checklist for each web server, CMS, database, container, control panel, or other app and include the security settings and maintenance that software requires.
Update your maintenance notes as the VPS changes. Remove checks for software you no longer use, add checks for new services, and keep the routine matched to what runs on the server.
All of the tutorial content on this website is subject to Hostinger's rigorous editorial standards and values.

Arif is a Technical Content Writer for Hostinger Tutorials with an educational background in Informatics. He specializes in Linux server administration, VPS hosting, and web development, and has authored more than 200 technical articles. Follow him on LinkedIn.

Minijus is a VPS Product Manager at Hostinger, focused on developing and improving products that help customers build and grow their online projects. Working at the intersection of technology, customer needs, and product development, he believes that curiosity, continuous learning, and challenging assumptions are essential to creating better products and experiences.